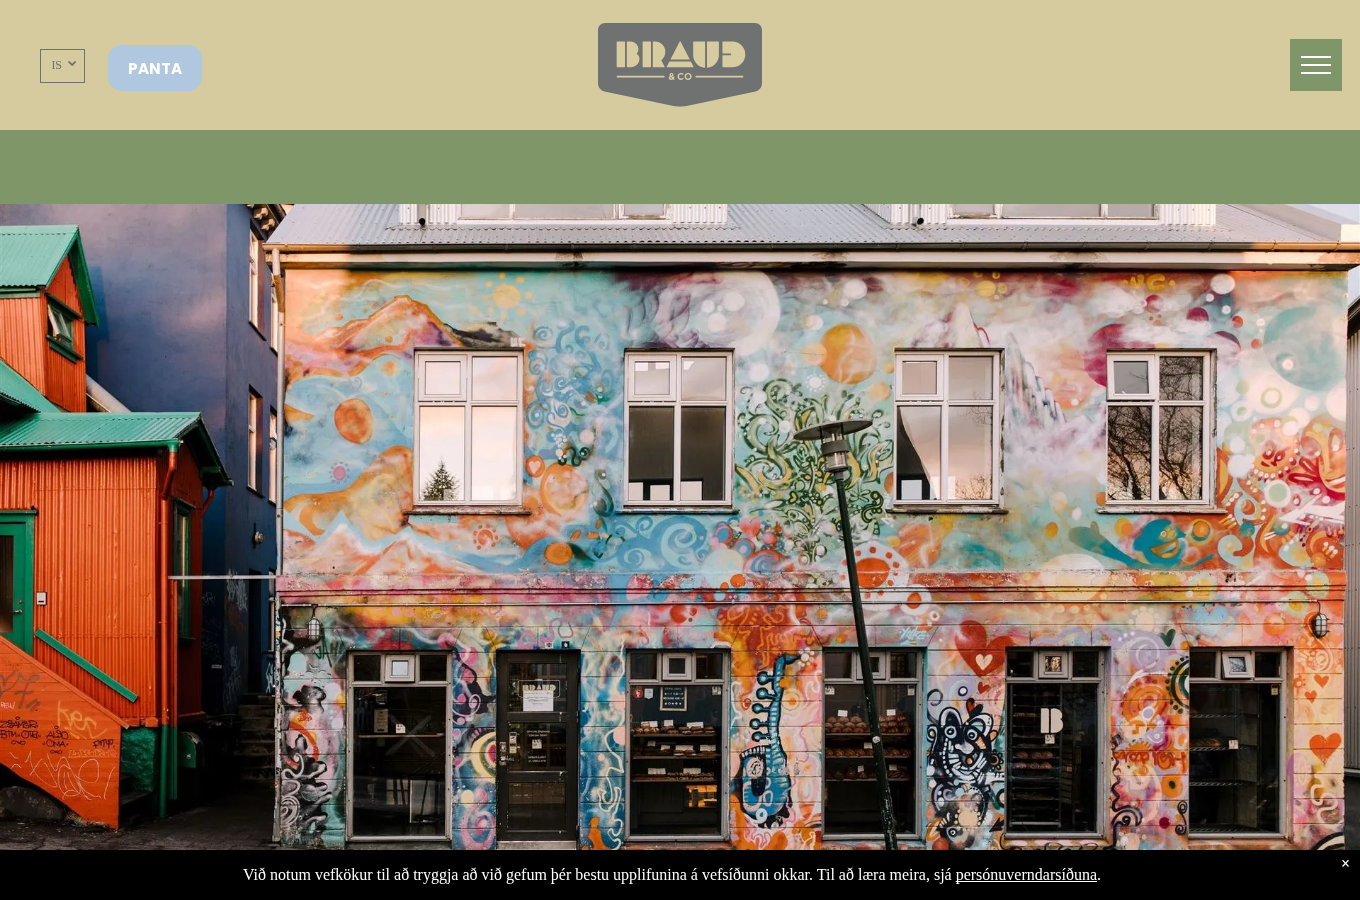
Scanned 10 Nov 2026, 15:27 UTC (Atlantic/Reykjavik, UTC+0). Homepage only. No consent button was clicked.
68out of 100 · first-load score
Needs attention
A few issues should be fixed so visitors get a fairer choice over cookies and tracking.
0 critical1 high1 medium2 low
This is not legal advice.
It is a point-in-time technical scan of a public homepage. It does not certify compliance with the GDPR,
ePrivacy rules, UK GDPR, CCPA/CPRA, or any other law. Dynamic tags, other pages, logged-in views,
and visits from other countries can look different. Have a qualified lawyer review your notices and
consent setup if you need a legal opinion.
At a glance
Platform
Duda (confidence 1.0)
HTTPS
Final URL is HTTPS; HTTP redirected to HTTPS
Consent banner
Visible on first load
Privacy policy link
Found (2)
Cookies on first load
5 total, 0 third-party
Known trackers / tags
4 vendor(s) matched
Third-party requests
55 across 9 host(s)
Google Consent Mode
No Consent Mode default detected
Consent platform
None detected from known vendor scripts
Homepage as loaded during the scan. No consent button was clicked.
Findings and copy-paste fixes
Each item includes steps for the detected platform and snippets a web person can paste. Test Accept, Reject, and “do nothing” in a fresh private window after you publish.
High
1. A banner is present, but cookies or trackers already ran
A consent banner was visible, yet the first load (with no click) already set 5 analytics/ads-style cookie(s) and loaded 4 known vendor(s). A banner that appears after tags have fired does not hold them back.
What to do: On Duda: Load Google tags, ads pixels, and session-replay scripts only after consent. Use a consent mode or tag-manager consent checks, and test with a fresh browser profile: Reject and 'do nothing' should both prevent non-essential cookies.
Written for Duda.
Duda’s built-in cookie notification is often an information bar (text + a close control) and does not delay marketing scripts. Replace it with a real choice: Accept and Reject (or essential only) at the same prominence.
In Site settings / Header HTML, paste the Consent Mode default above Google Tag Manager or Analytics.
Find every marketing script in custom header/footer code and widgets. Those scripts run on first load today — take them out of the global head.
Load the Meta Pixel only after Accept, using the snippet below. Leaving connect.facebook.net in the global header will keep firing before a choice.
Keep GTM in the head only if the Consent Mode default sits above it and GTM tags wait for granted signals. Otherwise load GA4 / Ads after Accept.
Edit the privacy / terms page so it lists cookies, purposes, and vendors, and link it from both the footer and the banner.
Test in a fresh private window: do nothing, click Reject, and click Accept. Only Accept should set analytics or ads cookies such as _ga, _gid, _gcl_au, _fbp.
Google Consent Mode v2 — default denied
Where: Site editor → Settings (or Site header HTML / Custom code) and paste in the <head>, above the Google Tag Manager or Analytics include. Publish when done.
<!-- Paste in the <head>, ABOVE any Google Tag Manager or gtag.js snippet. -->
<script>
  window.dataLayer = window.dataLayer || [];
  function gtag(){ dataLayer.push(arguments); }
  gtag('consent', 'default', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied',
    functionality_storage: 'granted',
    security_storage: 'granted',
    wait_for_update: 500
  });
</script>
After the visitor opts in
Where: Run from your banner’s Accept handler, after the default snippet is already on the page.
<!-- Call this only after the visitor opts in (Accept / save preferences). -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'granted',
    ad_user_data: 'granted',
    ad_personalization: 'granted',
    analytics_storage: 'granted'
  });
</script>
After the visitor rejects
Where: Run from the Reject / essential-only handler.
<!-- Call this when the visitor chooses Reject / essential only. -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied'
  });
</script>
Load the Meta Pixel only after marketing consent
Where: Remove the pixel from Site header/footer custom code and from any marketing widget that injects it on every page. Call loadMetaPixel() only after Accept. Duda’s built-in cookie notification does not, by itself, delay scripts.
<!-- Do not put the Meta Pixel in the <head> so it loads on every visit.
Load it only after marketing consent. Replace PIXEL_ID. -->
<script>
  function loadMetaPixel(pixelId) {
    if (window.fbq) return;
    !function(f,b,e,v,n,t,s){if(f.fbq)return;n=f.fbq=function(){n.callMethod?
    n.callMethod.apply(n,arguments):n.queue.push(arguments)};if(!f._fbq)f._fbq=n;
    n.push=n;n.loaded=!0;n.version='2.0';n.queue=[];t=b.createElement(e);t.async=!0;
    t.src=v;s=b.getElementsByTagName(e)[0];s.parentNode.insertBefore(t,s)}
    (window, document, 'script', 'https://connect.facebook.net/en_US/fbevents.js');
    fbq('init', pixelId);
    fbq('track', 'PageView');
  }
  // Example: after Accept / marketing opt-in
  // loadMetaPixel('PIXEL_ID');
</script>
Medium
2. Google tags loaded without a detectable Consent Mode default
Google Tag Manager, Analytics, or Ads requests were seen, but the scanner did not catch a gtag('consent', 'default', ...) call or equivalent dataLayer consent default before those tags ran.
What to do: On Duda: Set Google Consent Mode v2 defaults to denied for ad_storage, analytics_storage, ad_user_data and ad_personalization, then update them only after a visitor opts in. Place the default command before any gtag/GTM snippet.
Written for Duda.
On Duda, open the site-wide head / custom-code area described below and paste the default snippet first, before GTM or gtag.js.
Publish (or clear cache) and reload the homepage in a fresh private window. The default must fire before any google-analytics.com, googletagmanager.com, or doubleclick.net request.
Wire the Accept and Reject buttons to the update snippets. Reject must not fire the ‘granted’ update.
Google Consent Mode v2 — default denied
Where: Site editor → Settings (or Site header HTML / Custom code) and paste in the <head>, above the Google Tag Manager or Analytics include. Publish when done.
<!-- Paste in the <head>, ABOVE any Google Tag Manager or gtag.js snippet. -->
<script>
  window.dataLayer = window.dataLayer || [];
  function gtag(){ dataLayer.push(arguments); }
  gtag('consent', 'default', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied',
    functionality_storage: 'granted',
    security_storage: 'granted',
    wait_for_update: 500
  });
</script>
After the visitor opts in
Where: Banner Accept handler.
<!-- Call this only after the visitor opts in (Accept / save preferences). -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'granted',
    ad_user_data: 'granted',
    ad_personalization: 'granted',
    analytics_storage: 'granted'
  });
</script>
After the visitor rejects
Where: Banner Reject handler.
<!-- Call this when the visitor chooses Reject / essential only. -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied'
  });
</script>
Low
3. A privacy link exists, but no obvious cookie policy
Homepage privacy/legal links: Skilmálar; persónuverndarsíðuna. If cookies and third parties are only mentioned in passing, visitors may not get a clear list.
What to do: On Duda: Add a short cookie notice or a section in the privacy policy listing cookies, purposes, and vendors, and link it from the banner.
Written for Duda.
Add a cookie section, or a short cookie notice, that lists cookies, purposes, and vendors. This checkup is not a substitute for legal review.
You already have a legal page in some cases (for example a ‘Skilmálar’ / terms URL). Add a clear cookie list there, or a dedicated privacy page, and link it in the footer and the banner — not only as a small ‘learn more’ inside a notice.
Low
4. The banner text may not offer a clear reject option
Visible banner wording (truncated): Við notum vefkökur til að tryggja að við gefum þér bestu upplifunina á vefsíðunni okkar. Til að læra meira, sjá persónuverndarsíðuna. ×
What to do: On Duda: Where GDPR/ePrivacy applies, give reject or essential-only the same prominence as accept, and do not require a visit to a second layer just to say no.
Written for Duda.
Duda’s built-in cookie notification is often an information bar (text + a close control) and does not delay marketing scripts. Replace it with a real choice: Accept and Reject (or essential only) at the same prominence.
In Site settings / Header HTML, paste the Consent Mode default above Google Tag Manager or Analytics.
Find every marketing script in custom header/footer code and widgets. Those scripts run on first load today — take them out of the global head.
Load the Meta Pixel only after Accept, using the snippet below. Leaving connect.facebook.net in the global header will keep firing before a choice.
Keep GTM in the head only if the Consent Mode default sits above it and GTM tags wait for granted signals. Otherwise load GA4 / Ads after Accept.
Edit the privacy / terms page so it lists cookies, purposes, and vendors, and link it from both the footer and the banner.
Test in a fresh private window: do nothing, click Reject, and click Accept. Only Accept should set analytics or ads cookies such as _ga, _gid, _gcl_au, _fbp.
Google Consent Mode v2 — default denied
Where: Site editor → Settings (or Site header HTML / Custom code) and paste in the <head>, above the Google Tag Manager or Analytics include. Publish when done.
<!-- Paste in the <head>, ABOVE any Google Tag Manager or gtag.js snippet. -->
<script>
  window.dataLayer = window.dataLayer || [];
  function gtag(){ dataLayer.push(arguments); }
  gtag('consent', 'default', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied',
    functionality_storage: 'granted',
    security_storage: 'granted',
    wait_for_update: 500
  });
</script>
After the visitor opts in
Where: Run from your banner’s Accept handler, after the default snippet is already on the page.
<!-- Call this only after the visitor opts in (Accept / save preferences). -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'granted',
    ad_user_data: 'granted',
    ad_personalization: 'granted',
    analytics_storage: 'granted'
  });
</script>
After the visitor rejects
Where: Run from the Reject / essential-only handler.
<!-- Call this when the visitor chooses Reject / essential only. -->
<script>
  gtag('consent', 'update', {
    ad_storage: 'denied',
    ad_user_data: 'denied',
    ad_personalization: 'denied',
    analytics_storage: 'denied'
  });
</script>
Load the Meta Pixel only after marketing consent
Where: Remove the pixel from Site header/footer custom code and from any marketing widget that injects it on every page. Call loadMetaPixel() only after Accept. Duda’s built-in cookie notification does not, by itself, delay scripts.
<!-- Do not put the Meta Pixel in the <head> so it loads on every visit.
Load it only after marketing consent. Replace PIXEL_ID. -->
<script>
  function loadMetaPixel(pixelId) {
    if (window.fbq) return;
    !function(f,b,e,v,n,t,s){if(f.fbq)return;n=f.fbq=function(){n.callMethod?
    n.callMethod.apply(n,arguments):n.queue.push(arguments)};if(!f._fbq)f._fbq=n;
    n.push=n;n.loaded=!0;n.version='2.0';n.queue=[];t=b.createElement(e);t.async=!0;
    t.src=v;s=b.getElementsByTagName(e)[0];s.parentNode.insertBefore(t,s)}
    (window, document, 'script', 'https://connect.facebook.net/en_US/fbevents.js');
    fbq('init', pixelId);
    fbq('track', 'PageView');
  }
  // Example: after Accept / marketing opt-in
  // loadMetaPixel('PIXEL_ID');
</script>
Cookies set before any consent click
Rows highlighted amber are names commonly used for analytics, advertising, marketing, or session replay.
Headless Chromium loaded the homepage and waited for network activity to settle. No consent button was clicked. Cookies, third-party requests, banner text, privacy-policy links, HTTPS, and Google Consent Mode hooks were recorded on first load.
The automated score starts at 100 and subtracts for issues (critical −35, high −18, medium −8, low −3).
It is a triage aid, not a regulatory grade. Vendor names come from a built-in list of well-known hosts and cookie names; unknown scripts are listed only as third-party hosts. Platform detection is a best-effort match against public CMS signatures.
Limits.
This checkup loaded a single public URL in headless Chromium. It did not create an account, fill forms,
or click Accept/Reject. It may miss tags that fire later, on other pages, behind a paywall, or only in
certain regions. Cookie and request classification can be incomplete or occasionally wrong. The snippets
are starting points for a developer or designer — they are not a complete legal implementation.